Pre-Winter Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: validbest

Pass the CompTIA CySA+ CS0-003 Questions and answers with ValidTests

Exam CS0-003 All Questions
Exam CS0-003 Premium Access

View all detail and faqs for the CS0-003 exam

Viewing page 10 out of 11 pages
Viewing questions 136-150 out of questions
Questions # 136:

A security analyst identifies a device on which different malware was detected multiple times, even after the systems were scanned and cleaned several times. Which of the following actions would be most effective to ensure the device does not have residual malware?

Options:

A.

Update the device and scan offline in safe mode.

B.

Replace the hard drive and reimage the device.

C.

Upgrade the device to the latest OS version.

D.

Download a secondary scanner and rescan the device.

Expert Solution
Questions # 137:

An organization's email account was compromised by a bad actor. Given the following Information:

Which of the following is the length of time the team took to detect the threat?

Options:

A.

25 minutes

B.

40 minutes

C.

45 minutes

D.

2 hours

Expert Solution
Questions # 138:

A cybersecurity analyst is participating with the DLP project team to classify the organization's data. Which of the following is the primary purpose for classifying data?

Options:

A.

To identify regulatory compliance requirements

B.

To facilitate the creation of DLP rules

C.

To prioritize IT expenses

D.

To establish the value of data to the organization

Expert Solution
Questions # 139:

Patches for two highly exploited vulnerabilities were released on the same Friday afternoon. Information about the systems and vulnerabilities is shown in the tables below:

Question # 139

Which of the following should the security analyst prioritize for remediation?

Options:

A.

rogers

B.

brady

C.

brees

D.

manning

Expert Solution
Questions # 140:

Which Of the following techniques would be best to provide the necessary assurance for embedded software that drives centrifugal pumps at a power Plant?

Options:

A.

Containerization

B.

Manual code reviews

C.

Static and dynamic analysis

D.

Formal methods

Expert Solution
Questions # 141:

A security analyst is investigating an unusually high volume of requests received on a web server. Based on the following command and output:

access_log - [21/May/2024 13:19:06] "GET /newyddion HTTP/1.1" 404 -

access_log - [21/May/2024 13:19:06] "GET /1970 HTTP/1.1" 404 -

access_log - [21/May/2024 13:19:06] "GET /dopey HTTP/1.1" 404 -

...

Which of the following best describes the activity that the analyst will confirm?

Options:

A.

SQL injection

B.

Directory brute force

C.

Remote command execution

D.

Cross-site scripting

Expert Solution
Questions # 142:

Which of the following can be used to learn more about TTPs used by cybercriminals?

Options:

A.

ZenMAP

B.

MITRE ATT&CK

C.

National Institute of Standards and Technology

D.

theHarvester

Expert Solution
Questions # 143:

A Chief Information Security Officer (CISO) wants to disable a functionality on a business-critical web application that is vulnerable to RCE in order to maintain the minimum risk level with minimal increased cost.

Which of the following risk treatments best describes what the CISO is looking for?

Options:

A.

Transfer

B.

Mitigate

C.

Accept

D.

Avoid

Expert Solution
Questions # 144:

Which of the following is the best framework for assessing how attackers use techniques over an infrastructure to exploit a target’s information assets?

Options:

A.

Structured Threat Information Expression

B.

OWASP Testing Guide

C.

Open Source Security Testing Methodology Manual

D.

Diamond Model of Intrusion Analysis

Expert Solution
Questions # 145:

A cybersecurity team lead is developing metrics to present in the weekly executive briefs. Executives are interested in knowing how long it takes to stop the spread of malware that enters the network.

Which of the following metrics should the team lead include in the briefs?

Options:

A.

Mean time between failures

B.

Mean time to detect

C.

Mean time to remediate

D.

Mean time to contain

Expert Solution
Questions # 146:

Which of the following is the best reason to implement an MOU?

Options:

A.

To create a business process for configuration management

B.

To allow internal departments to understand security responsibilities

C.

To allow an expectation process to be defined for legacy systems

D.

To ensure that all metrics on service levels are properly reported

Questions # 147:

Which of the following documents sets requirements and metrics for a third-party response during an event?

Options:

A.

BIA

B.

DRP

C.

SLA

D.

MOU

Questions # 148:

A vulnerability scan shows the following vulnerabilities in the environment:
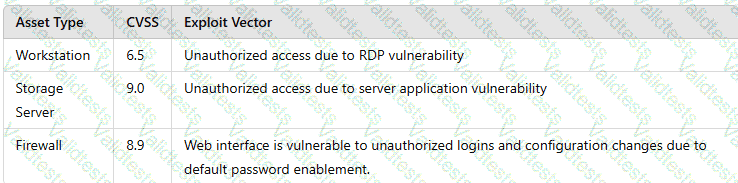
Question # 148

At the same time, the following security advisory was released:

"A zero-day vulnerability with a CVSS score of 10 may be affecting your web server. The vendor is working on a patch or workaround."

Which of the following actions should the security analyst take first?

Options:

A.

Contact the web systems administrator and request that they shut down the asset.

B.

Monitor the patch releases for all items and escalate patching to the appropriate team.

C.

Run the vulnerability scan again to verify the presence of the critical finding and the zero-day vulnerability in the environment.

D.

Forward the advisory to the web security team and initiate the prioritization strategy for the other vulnerabilities.

Questions # 149:

The DevSecOps team is remediating a Server-Side Request Forgery (SSRF) issue on the company's public-facing website. Which of the following is the best mitigation technique to address this issue?

Options:

A.

Place a Web Application Firewall (WAF) in front of the web server.

B.

Install a Cloud Access Security Broker (CASB) in front of the web server.

C.

Put a forward proxy in front of the web server.

D.

Implement MFA in front of the web server.

Questions # 150:

A security administrator needs to import Pll data records from the production environment to the test environment for testing purposes. Which of the following would best protect data confidentiality?
Options:

A.

Data masking

B.

Hashing

C.

Watermarking

D.

Encoding

Viewing page 10 out of 11 pages
Viewing questions 136-150 out of questions